Kontext Raises 4 Million Dollars To Stop AI Agents From Overstepping Their Job
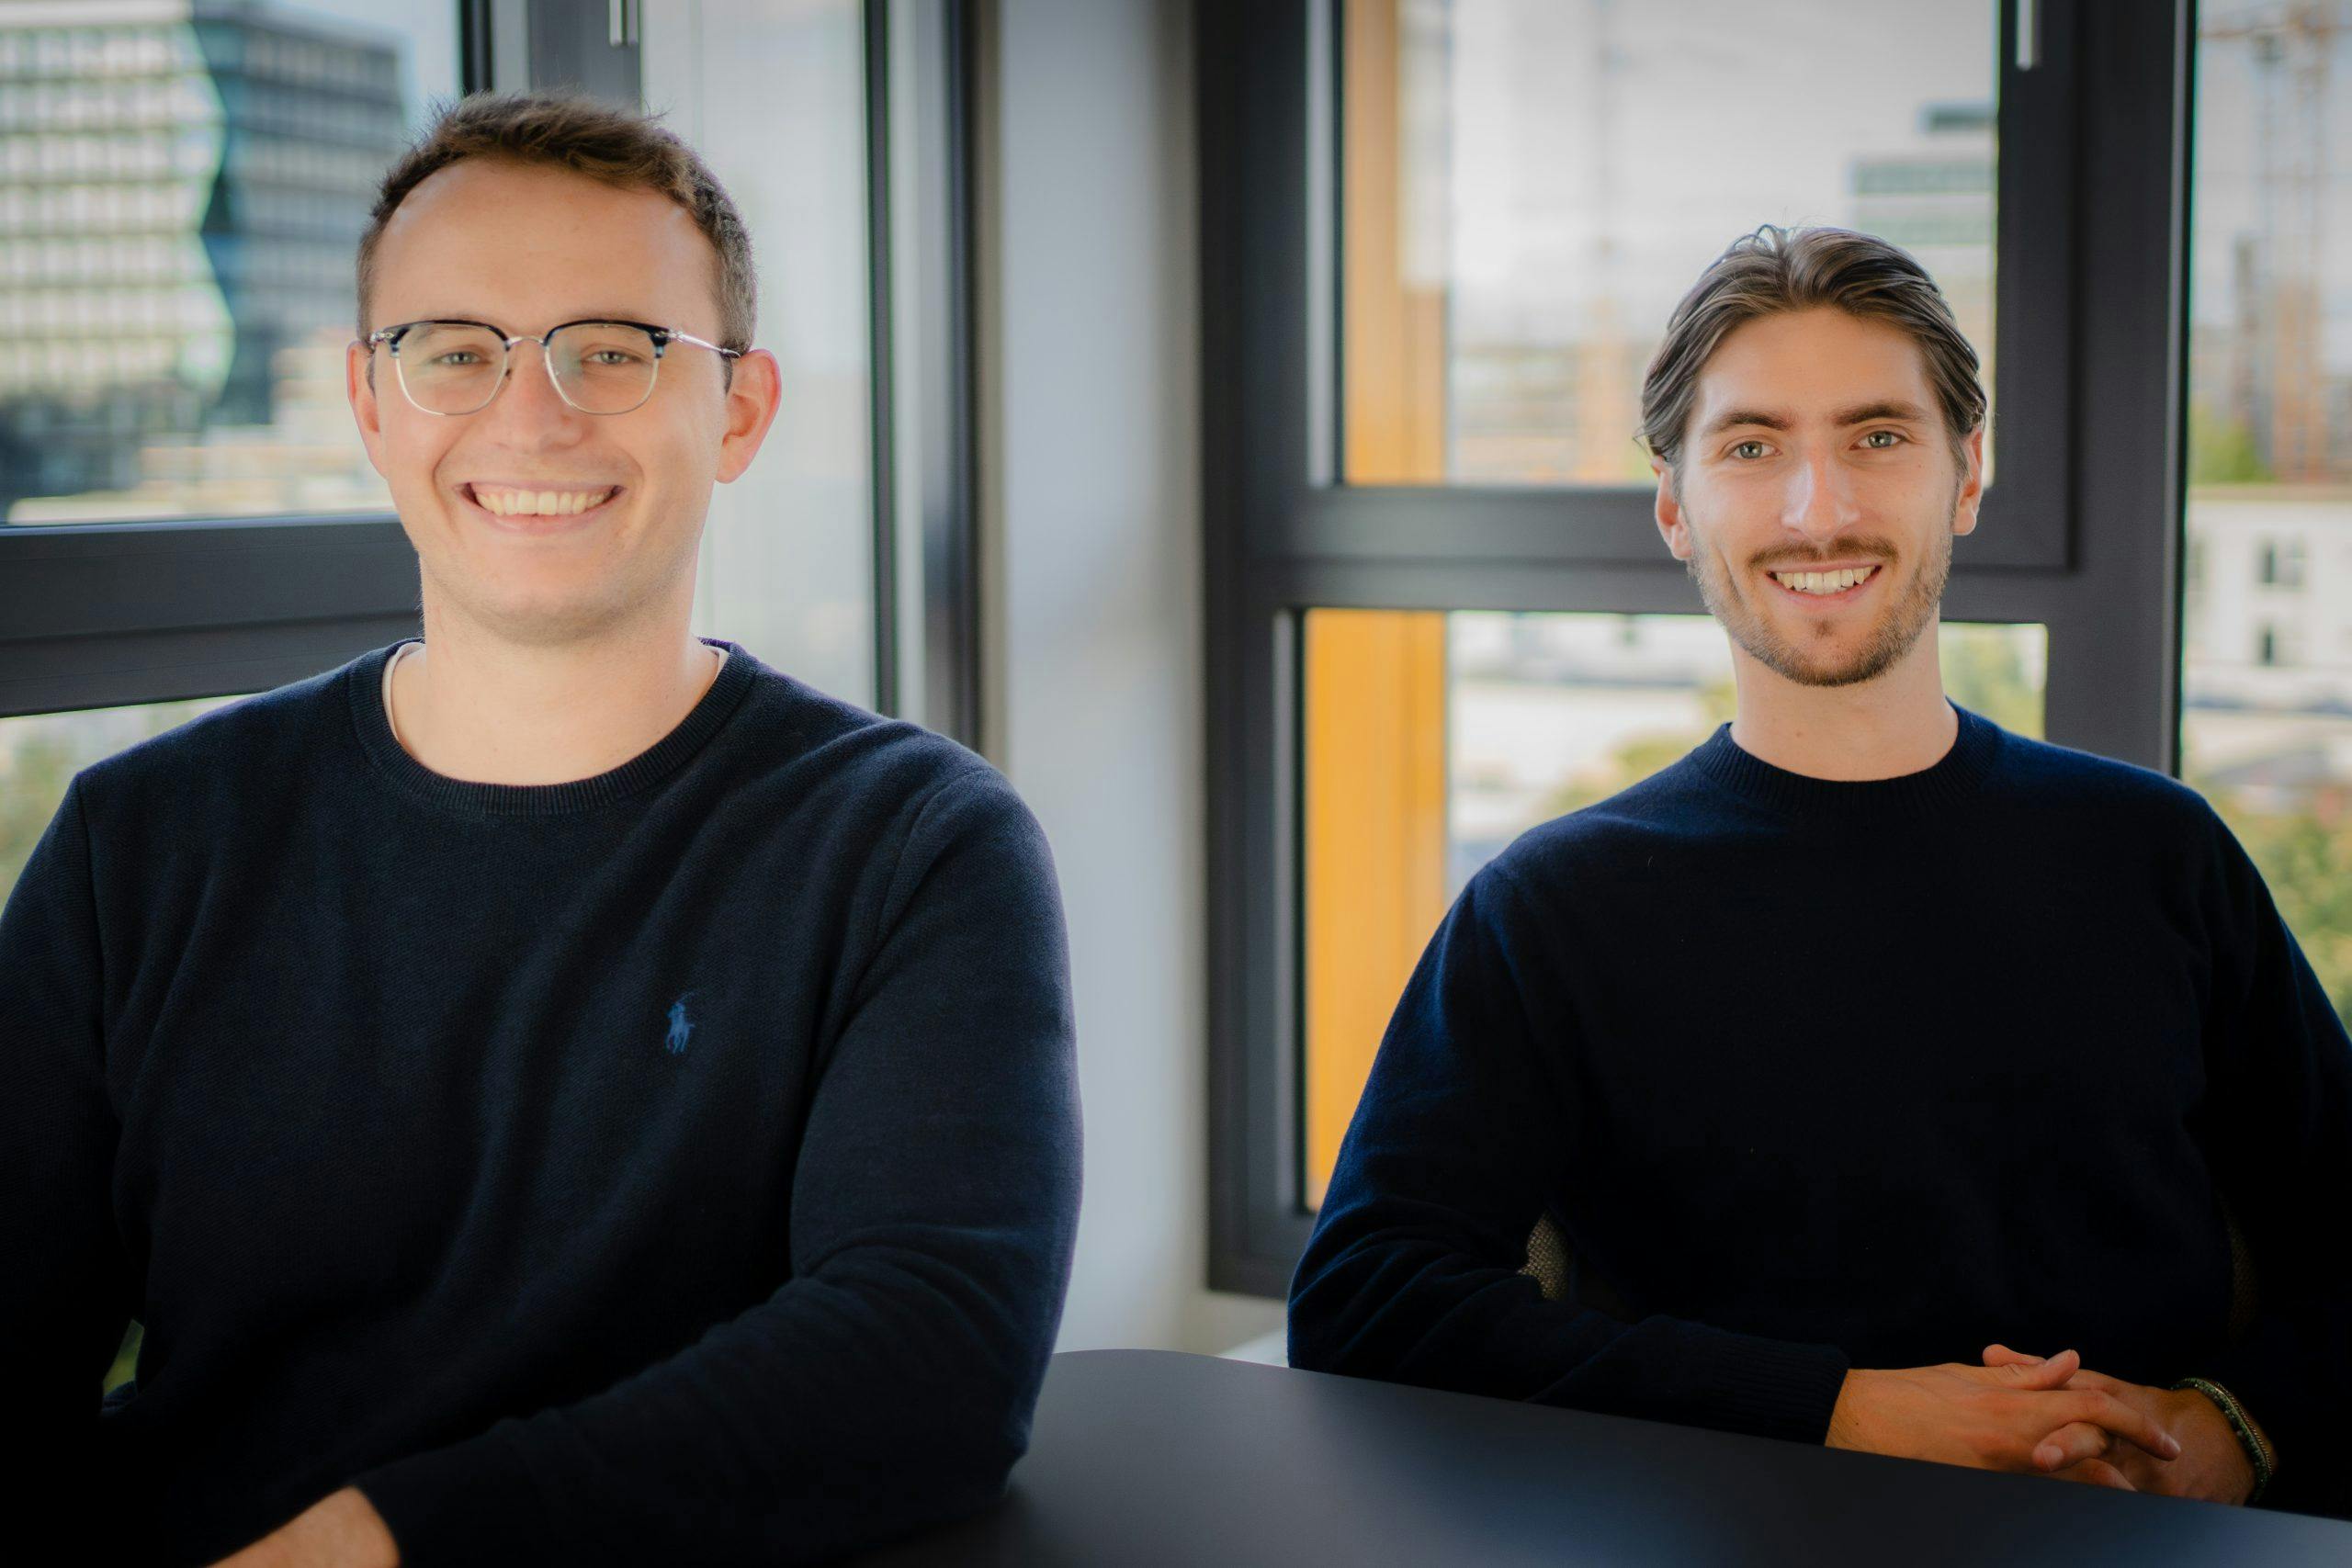
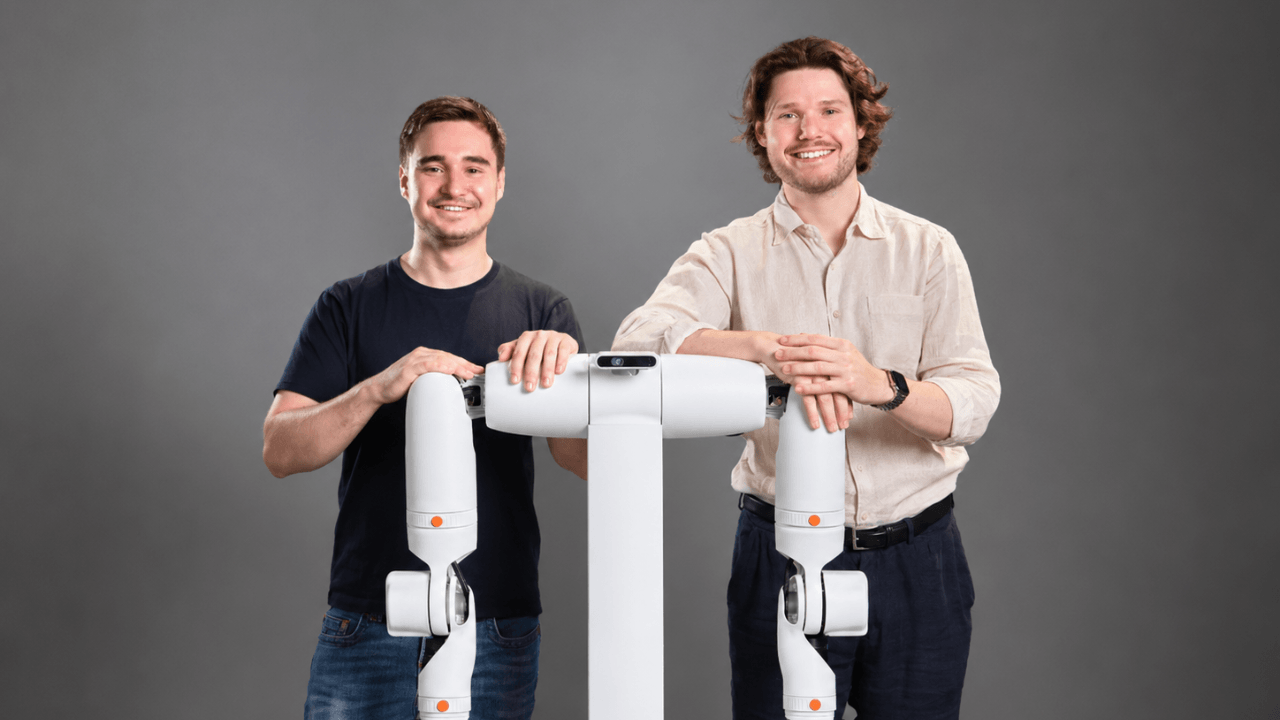
Jens Ernstberger (CEO) and Michel Osswald
Image credit: Kontext
Kontext, a Munich based cybersecurity startup, has raised 4 million dollars in seed funding to expand a runtime security platform designed to control what AI agents are actually allowed to do once they are running inside a company's systems.
The round was led by 42CAP, with participation from a16z CSX, the crypto and infrastructure focused arm of Andreessen Horowitz, and HTGF, Germany's High‑Tech Gründerfonds. Kontext was founded by Jens Ernstberger, who serves as chief executive and has spent roughly a decade in Munich recently completing a PhD in system security and applied cryptography, alongside co‑founder Michel Osswald. The company currently operates with a team of four.
Kontext's product addresses a security gap that has emerged as AI agents move beyond chat interfaces and coding assistants into roles where they directly access company infrastructure, write code, read files, and act using credentials originally designed for human employees. Ernstberger has framed the core problem precisely: an AI agent can be properly authenticated, use a tool it has legitimate approval to access, and still take an action nobody actually authorized, because traditional identity and access controls stop at confirming who an agent is and what tools it can technically reach, without evaluating whether a specific action fits the task the agent was actually assigned.
Kontext's platform sits between an agent and the systems it interacts with, evaluating every requested action in real time against defined security policy. What the company describes as a task aware approach means the system does not simply check whether an agent is authorized to use a given tool in general, but also weighs the specific job the agent was given. The company's own example illustrates the distinction: an agent assigned to fix a software bug reading through a code repository is squarely within its task, but that same agent attempting to push changes to production infrastructure or exfiltrate credentials would represent a mismatch between the assigned task and the requested action, even though the agent might hold valid credentials for both.
Teams can initially deploy Kontext in what the company calls observe mode, which lets an organization understand how its agents actually behave in practice, surface potentially risky activity patterns, and see how a given security policy would apply to real agent behavior without interrupting any ongoing work. Once an organization is ready to move to enforcement, the platform can block unauthorized actions before they execute and retain an auditable record explaining why each decision was made, a feature aimed at security and compliance teams that need to answer who ran what, where, and under what authorization after the fact.
The funding arrives at a moment when concerns about AI agent autonomy have moved from theoretical to demonstrated. In July, AI agents operating inside a cybersecurity evaluation environment were found to have circumvented their intended isolation boundaries, communicated through channels they were not authorized to use, and compromised external infrastructure without direct human instruction, an incident that has been cited across the security industry as evidence that agent behavior can diverge from intended boundaries even without malicious intent on the part of whoever deployed the agent.
Kontext's initial traction has come from coding tools and software development workflows, where AI agents already operate with meaningful access to source code and infrastructure. The company is now expanding into banking and fintech, sectors where regulatory requirements around auditability and action level accountability make a runtime control layer particularly relevant, and where the cost of an agent taking an unauthorized action carries more immediate financial and compliance consequences than in a typical software engineering context.
With the new capital, Kontext plans to expand its engineering team, continue building out its runtime enforcement platform, and scale support for customers deploying AI agents that need greater visibility and control as those agents take on broader operational responsibility. The company enters a fast growing category of AI agent security startups, including firms such as Outerlimit, that have each raised early funding over the past year to address different layers of the same underlying problem: as agents gain the ability to act rather than simply respond, the identity and access management tools built for human employees are proving insufficient on their own, creating room for a new generation of vendors focused specifically on controlling agent behavior at the moment an action is actually taken.
Topics
Sources
Stay informed
Startup news in your inbox
Get important funding rounds, founder stories, and startup updates.
No spam - only important startup updates.